Solution proposals

Trusted PalmID: verification at service points

A palm-identity layer for apps, POS and service points. The journey covers identity establishment, enrolment, activation and subsequent verification; partners retain membership, attendance and payment decisions.

V336 pagesVietnamese PDFProposal / scope to confirm
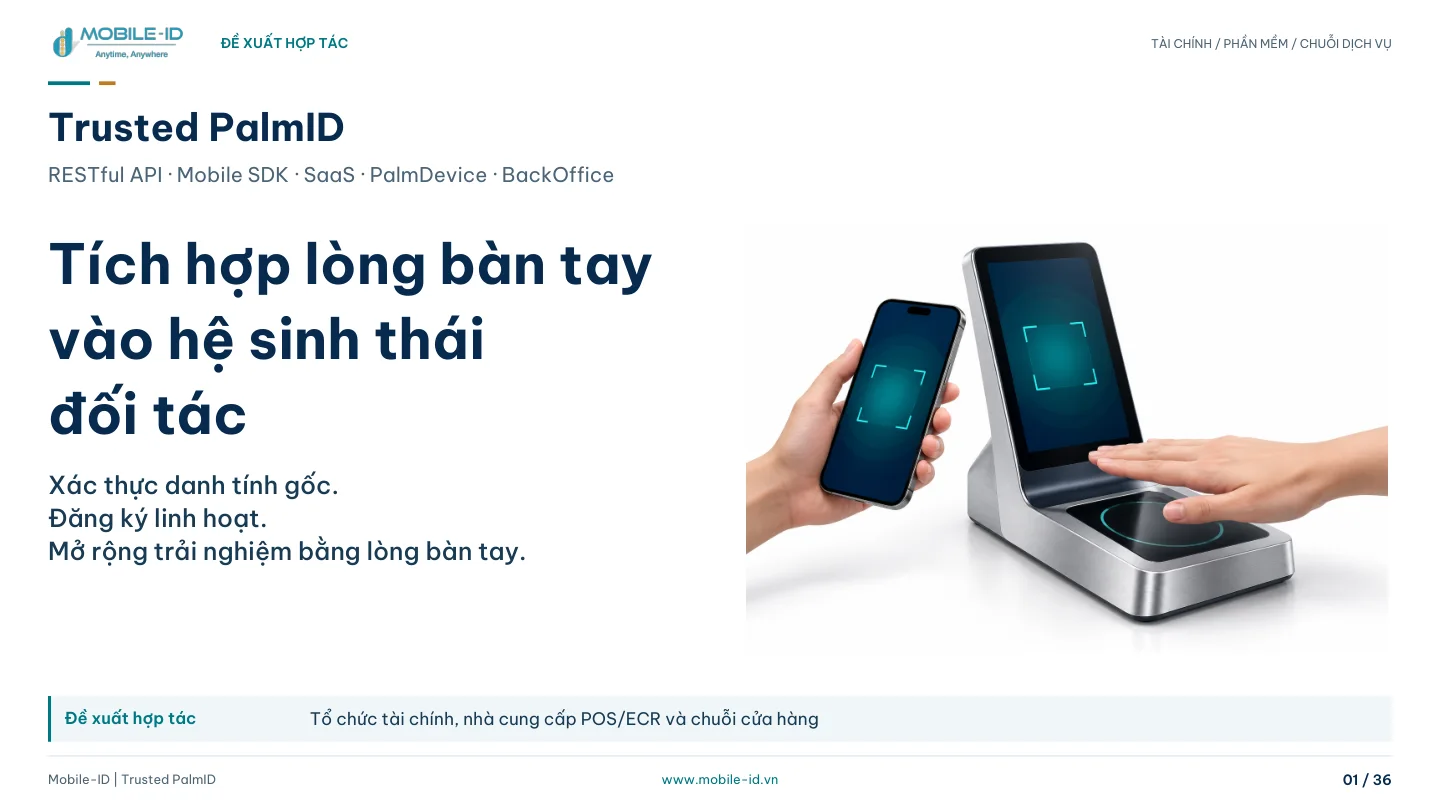
Vietnamese PDF cover: Trusted PalmID: verification at service points
Original document cover · language unchanged
01 / THE CHALLENGE

Why this approach?

An identification result does not itself establish membership benefits or payment authority. Organisations, devices, merchants and purposes must be correctly linked before activation.

02 / Scope

The proposed solution layers

01

Two enrolment routes: mobile palmprint first or PalmDevice capture, with separate palmvein completion conditions.

02

SaaS, SDK/API and BackOffice under the agreed scope.

03

Partner applications consume results and apply business policy.

Keep responsibilities explicit

Mobile-ID

Infrastructure components, applicable documentation and integration support within the agreed scope.

Customer / partner

Business systems, permitted data, decision authority and end-to-end acceptance.

Other participating parties

CAs, banks, device suppliers or data sources as applicable; confirm connection rights and conditions separately.

Before getting started

  1. Agree identity establishment, capture permissions, devices and alternatives.
  2. Agree OS, SDK, firmware, merchant binding and data permissions.

Readiness

The source is a proposal. Product scope, release, SDK/API, connections and usage rights require confirmation for the deployment combination; diagrams and mockups do not establish production readiness.

03 / A TESTABLE PILOT

Start small. Verify the whole journey.

Select one service point and use case. Test enrolment, activation, failed verification, revocation and disconnection; the partner confirms business outcomes independently.

Discuss pilot scope
04 / READ AND PRESENT

The proposal, in context.

Lightweight offline WebP presentation. The original PDF opens only when you choose it.

Page 1 · Vietnamese PDF

Vietnamese presentation · the PDF has not been translated.

Read for the decision you need

Source document

The editorial summary is based on the sections linked above. The original PDF is unchanged. An observed version is not confirmation of current commercial status.

Open source document · online
Original filenameMobileID_TrustedPalmID_Integration_Proposal_V3 1.pdf

Markdown summary

Related content

Sign-in & authentication

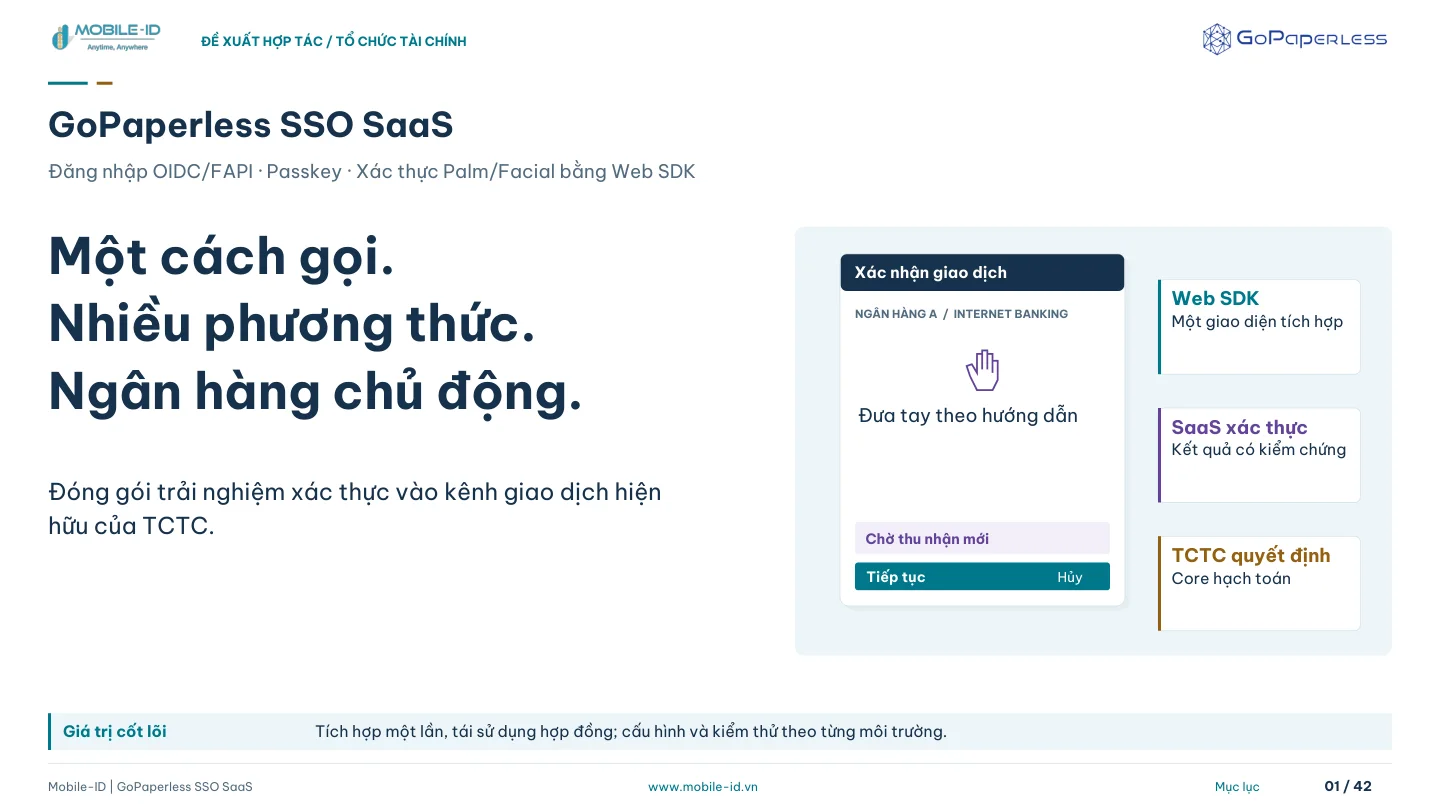
GoPaperless SSO SaaS for banking

A proposal for adding OIDC/FAPI and Passkey sign-in and Palm/Facial verification to an existing banking channel. Three integration points are separated: BFF for sign-in, Web SDK for interaction and Backend for evidence validation. Transaction decisions and posting remain with the financial institution.

42 pages · Vietnamese PDF
Next step

Where does your project begin?

Share your current systems and intended outcomes to plan the next integration step.

Discuss your project